Simplify IT Asset Management and unify your inventory
What is an IT Audit? Process, Best Practices, And Checklist
An IT audit, or information technology audit, is a systematic review of an organization's IT systems, processes, and controls. Its main goal is to check if your IT infrastructure is secure, efficient, compliant with regulations, and aligned with your business objectives.
Any company that relies on technology (from small businesses to large enterprises) can benefit from regular IT audits. They help uncover risks, improve internal controls, and ensure your IT environment runs smoothly and safely.
Key takeaways
- An IT audit is a systematic review of your organization's IT systems, processes, and controls to verify they are secure, compliant, and aligned with business goals.
- Regular audits deliver three core benefits: stronger security, regulatory compliance, and higher operational efficiency.
- The IT audit process runs through four key phases: planning, fieldwork, analysis, and reporting.
- A reliable, up-to-date asset inventory is the starting point of any audit.
- Audits can be performed by internal teams or certified third parties, depending on your compliance requirements.
- Most organizations run a full IT audit once a year and conduct focused reviews on high-risk areas every quarter.
Why are IT audits important?
IT audits are important because they help organizations find and fix weaknesses in their technology before they turn into costly problems. By reviewing systems, processes, and security controls, audits make sure that data is protected and IT operations run smoothly.
In some industries (like finance, healthcare, or government), regular audits are mandatory to meet strict regulations and protect sensitive information. But even when not required by law, proactive IT audits are a smart way to catch risks early, prove compliance, improve efficiency, and build trust with customers and partners.
5 benefits of an information technology audit
Regular IT audits bring real value to your organization. Here are five key benefits you can expect:
- Stronger security: Uncover and fix vulnerabilities like weak passwords, outdated software, or misconfigured systems.
- Regulatory compliance: Meet industry standards and avoid fines by proving that your IT controls follow laws and frameworks like GDPR (General Data Protection Regulation), HIPAA (Health Insurance Portability and Accountability Act), and PCI DSS (Payment Card Industry Data Security Standard). The NIST Cybersecurity Framework is another widely adopted reference for aligning IT controls with security requirements.
- Higher efficiency: Spot redundant tools or manual tasks so you can streamline processes and reduce costs.
- Better business continuity: Test backups and disaster recovery plans to ensure your company stays up and running during disruptions.
- Informed decision-making: Use audit insights to guide IT investments and align technology with your business goals.
Types of IT audits
There isn't just one way to audit your IT environment. Organizations can perform different types of IT audits depending on who conducts them and what they want to achieve. Knowing these categories, as covered in the information technology audit Wikipedia article, helps you plan the right audit at the right time.
| Type | Purpose | Who typically performs it | Typical deliverables |
|---|---|---|---|
| Internal | Monitor controls, catch risks early, prepare for inspections | Internal IT team, compliance officers | Internal report, action plan |
| External | Independent assessment of security and compliance posture | Certified third-party firms | Formal audit report, certification |
| Compliance | Verify adherence to laws, regulations, and standards | Internal or external auditors | Compliance certificate, audit findings |
| Controls/Risk | Evaluate how well internal IT controls reduce risks | Risk managers, internal auditors | Risk register, control assessment |
| Operational | Check efficiency and reliability of IT operations | IT operations team, internal auditors | Process review, efficiency report |
| System/Application | Review specific systems for security and functionality | IT specialists, application auditors | System audit report, vulnerability list |
| SDLC | Examine IT project planning, development, testing, and deployment | Development and QA teams, auditors | SDLC review report, project assessment |
IT audit types based on who performs them
Internal IT audits are performed by your own staff. This usually means your IT team, internal auditors, or compliance officers. They help you monitor systems, catch risks early, and prepare for official inspections or certifications.
External IT audits are carried out by independent, certified third-party firms. Many organizations hire them voluntarily to get an unbiased assessment of their security and compliance posture. This adds credibility and helps build trust with customers and partners.
In some cases, external audits are mandatory. For example, when a regulator requires proof of compliance, or when a client contract demands an official certification like SOC 2 (System and Organization Controls 2) or ISO 27001 (the international standard for Information Security Management Systems). Whether optional or required, external audits confirm that your internal checks really work and meet industry standards.
Types of IT audits by purpose
Depending on what you want to check, IT audits can be divided into a few main categories:
- Compliance audits. Make sure your company follows laws, regulations, and industry standards. These audits are essential for sectors like healthcare, finance, and e-commerce.
- Controls or risk audits. Evaluate how well your internal IT controls work and whether they reduce risks effectively. This type helps you spot gaps in security, Access Management, and policies. A Governance, Risk, and Compliance (GRC) framework can support this type of audit by providing a structured approach to managing risks and controls.
- Operational audits. Focus on how efficient and reliable your IT operations are. A hardware audit is a clear example of this type: it checks which devices are still in use, which are ready for refresh, and which should be retired.
- System or application audits. Review specific systems or software to confirm they work properly, are secure, and meet user needs. A software audit is a common case. It checks software versions, licenses, usage, and whether you are compliant with vendor agreements.
- Development lifecycle (SDLC) audits. Examine how new IT projects or system updates are planned, built, tested, and deployed. This ensures good Project Management and reduces risks during major changes.
IT audit checklist
Having an IT audit checklist is a smart way to stay organized and make sure you don't overlook any important steps. It gives your team a clear roadmap, saves time, and helps you adapt the process to your company's size and industry.
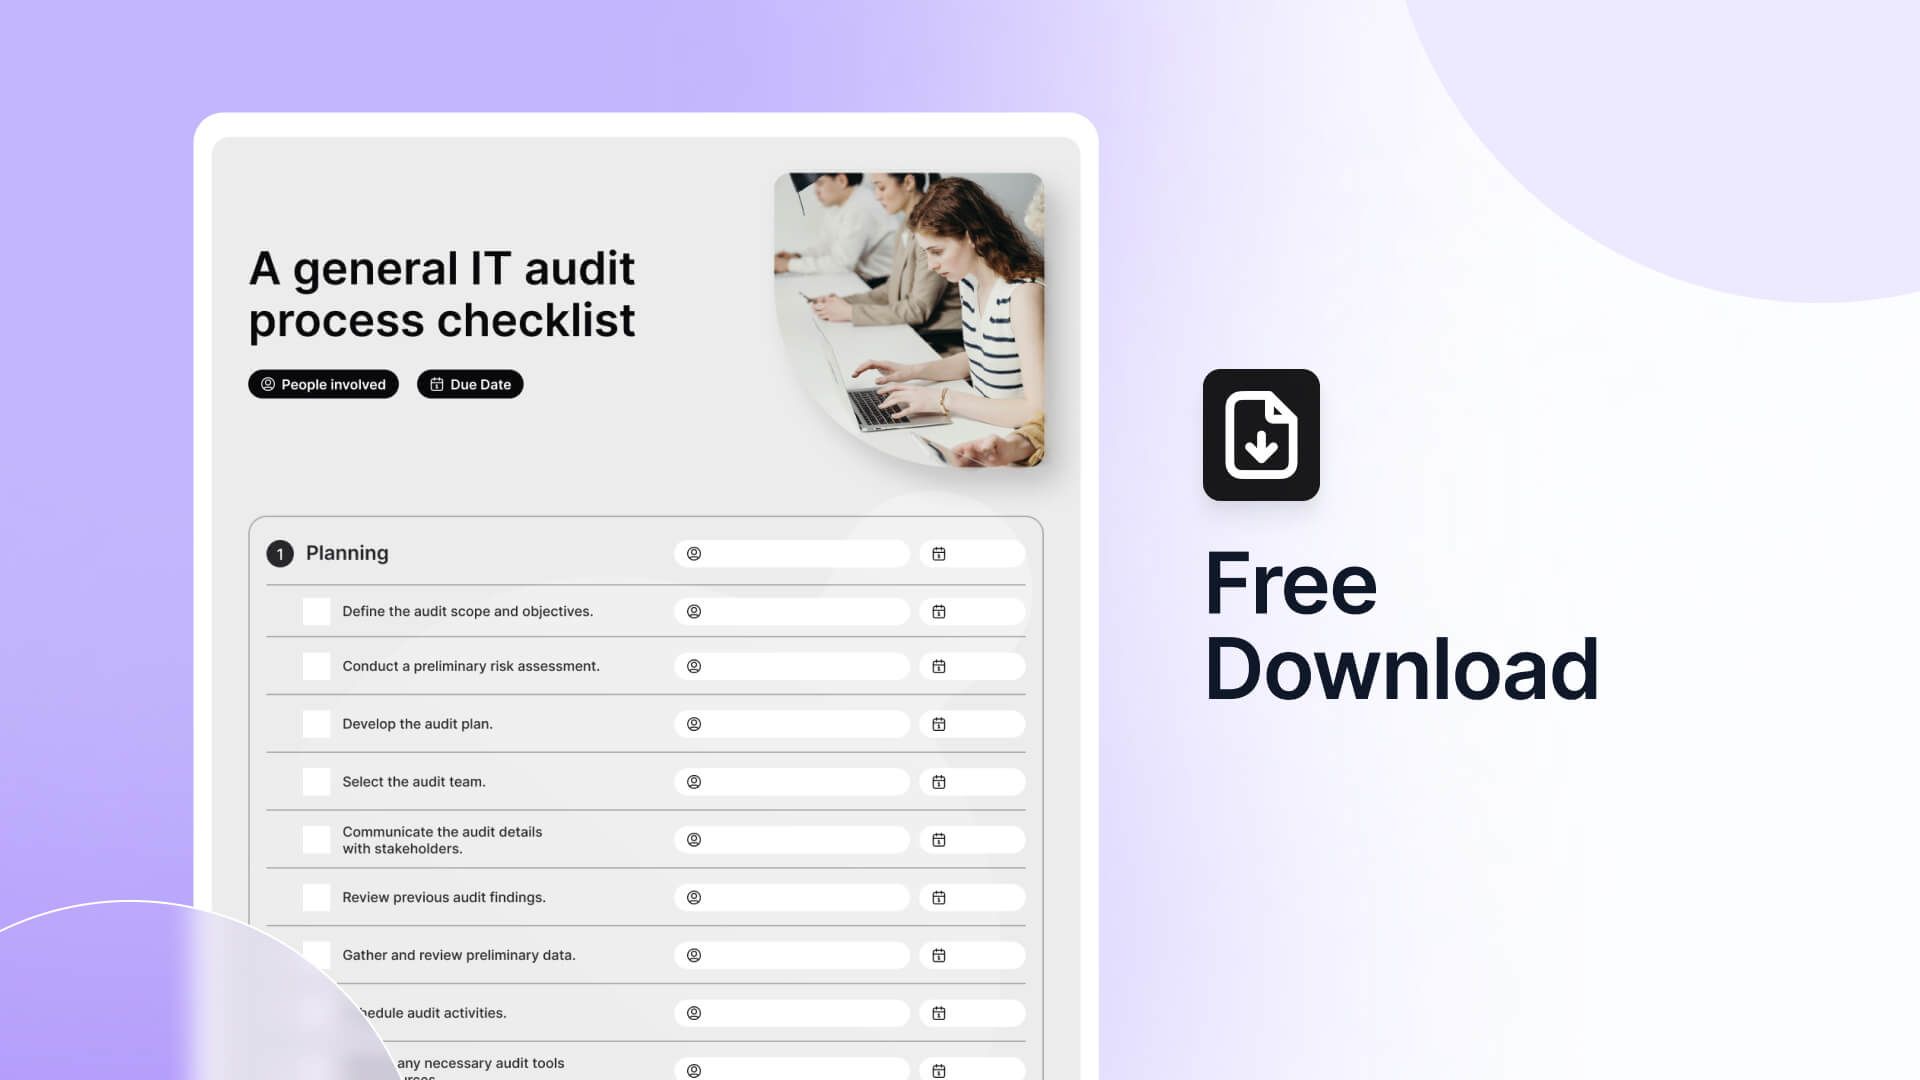
We've put together a free download with two general IT audit checklists: one lists the main activities to cover at each stage, and the other provides key questions to guide your review. Use them as a starting point and customize them to match your specific audit goals.
Download your IT audit checklist
Includes two general IT audit checklists that will guide you through the main stages of the process.
What happens in an IT audit? The IT audit process

Understanding the IT audit lifecycle helps teams plan ahead and reduces the time spent gathering evidence during fieldwork. A typical IT audit follows a series of clear steps to check how well your systems, data, and controls are managed.
Before diving into the steps, it helps to know how long the process takes. A full IT audit can take anywhere from 2 to 5 days for a small business, 1 to 3 weeks for a mid-market company, and 4 to 8 weeks or more for an enterprise environment. Scope, team size, and documentation readiness all affect the final timeline.
While every audit is different, these steps provide a solid roadmap. You can use our downloadable IT audit checklist alongside each phase to stay on track.
- Planning. Set the scope and objectives of the audit based on risks, company goals, and legal requirements. Allocate resources and choose the audit team.
- Preliminary review. Learn how your current IT systems and controls work. Gather background information and review past audits to spot areas that need special attention. Your CMDB (Configuration Management Database) can provide a complete, structured picture of your IT environment at this stage.
- Risk assessment. Identify potential risks and vulnerabilities. Analyze how likely they are and what impact they could have, then prioritize them.
- Audit development. Design audit procedures and set criteria to check if controls are working as intended. Plan exactly how you will collect evidence.
- Fieldwork and testing. Carry out the audit plan. Interview staff, review documents, observe processes, and run technical tests to gather solid evidence.
- Analysis and evaluation. Analyze the information you collected to see if controls are effective. Pinpoint weaknesses, gaps, or non-compliance areas.
- Reporting. Write an audit report that clearly explains your findings, conclusions, and practical recommendations for fixing any issues. Centralizing policies, change records, and incident history in a service Management platform like InvGate Service Management makes evidence collection considerably faster.
- Review and finalization. Discuss the draft report with stakeholders, make final edits, and share the completed report. Plan follow-up actions to track progress.
The IT audit team
A well-structured team makes an IT audit more efficient and reliable. Whether you handle audits internally or bring in external experts, defining clear roles ensures everyone knows what to do at each stage.
This is especially important because 89% of internal audit teams say hiring and retaining skilled auditors is challenging, according to the Caseware 2024 Internal Audit Trends Report.
This shortage comes from the high demand for professionals with both traditional audit expertise and newer skills like data analytics and cybersecurity, combined with a tight job market and expanding audit scopes.
The right mix of internal talent and trusted specialists helps cover all technical and compliance needs without gaps. Team size also varies by organization. Small organizations may run audits with 1 to 2 people. Mid-market companies typically work with 3 to 5. Enterprise audits often involve 5 to 10 people, including external specialists.
Here are the main roles and their key responsibilities:
- IT auditor: Plans and performs the audit activities, collects and analyzes evidence, tests controls, and documents findings.
- Audit manager or lead auditor: Oversees the entire audit process, coordinates the team's work, ensures deadlines are met, and reviews the final report for quality and accuracy.
- IT specialist: Provides technical expertise on systems, networks, and security. Supports testing, vulnerability scanning, and reviewing complex configurations.
- Compliance officer: Helps align the audit with regulatory requirements, assists in risk assessment, and verifies that the audit covers all compliance areas.
- Stakeholders and process owners: Not part of the audit team itself, but they supply information, answer questions, and help implement any recommended improvements.
When internal expertise is not enough, hire a third-party auditor and keep your internal team involved to ensure context and continuity.
Best practices for IT auditing
Following some proven best practices can make your IT auditing process more effective, repeatable, and less stressful. Here are five tips to keep your audit process on track.
1. Define clear objectives and scope
Before starting any audit, be clear about what you want to achieve and which areas you will examine. A well-defined scope helps you focus resources where they matter most and avoids wasting time on irrelevant details.
2. Take a risk-based approach
Not all systems and processes carry the same level of risk. Identify your most critical assets and high-risk areas first, and allocate extra attention to them during planning, testing, and reporting.
3. Keep detailed documentation
Document every step: audit plans, test procedures, evidence collected, and final reports. Good records make it easy to justify findings, demonstrate standards adherence, and speed up future audits.
4. Select the right software
Choose tools that make the audit process smoother and more accurate. Dedicated IT audit software helps organize tasks and evidence. An IT Asset Management solution like InvGate Asset Management keeps the inventory and asset data your audit relies on accurate and up to date.
5. Follow up on recommendations
An audit isn't finished when the report is delivered. Track the status of your action plans, verify that issues are resolved, and schedule follow-up reviews to confirm improvements stick.
How to streamline IT audits with InvGate Asset Management
Performing an IT audit is much easier when your data is complete, accurate, and always up to date. InvGate Asset Management gives you a unified view of all your IT Asset Management data: hardware, software, and configuration details, all in one place.
A reliable, up-to-date inventory is the starting point of any audit. With automation, you can collect and update asset data with minimal manual effort.
Here are the key features that support a smooth IT audit:
- Complete Inventory Management: Build a full asset inventory in as little as 24 hours in environments where agents and network discovery can be deployed across the network. This includes hardware, software, and Configuration Management data in a single, unified view.
- Software compliance tracking: Monitor license usage and detect non-compliant or unused installations before they become an issue.
- Lifecycle and depreciation tracking: Keep tabs on each asset's condition, value, and replacement needs, supporting financial and operational audit requirements.
- Automated alerts and health rules: Get notified about potential risks or anomalies that might need attention during an audit.
- Custom reports and dashboards: Generate audit-ready reports and share key insights with stakeholders quickly and easily.
InvGate Service Management complements this by centralizing your IT policies, change requests, and incident history. This gives auditors documented evidence of how your processes work and how issues are resolved.
Once your audit workflow is in place, the next step is making sure your team has the credentials to back it up. The following section covers the most recognized certifications in IT auditing.
IT audit certifications
Pursuing an industry-recognized certification can give you a competitive edge in IT auditing. Certifications validate your knowledge, help you stay up to date with best practices, and prove your skills to employers and clients alike.
Here are some of the most relevant options to consider.
1. Certified Information Systems Auditor (CISA)
The Certified Information Systems Auditor (CISA) certification, offered by ISACA, is one of the most trusted credentials for IT auditors worldwide. It covers key areas like auditing processes, governance, Risk Management, and information system security controls.
Getting a CISA demonstrates that you have the experience and expertise to assess vulnerabilities, report on compliance, and implement effective controls. It's highly recommended for IT audit professionals, audit managers, and consultants.
2. Certified Information Security Manager (CISM)
Also from ISACA, the Certified Information Security Manager (CISM) certification focuses on managing and governing an organization's information security program. It bridges the gap between technical security knowledge and high-level business objectives.
CISM is valuable for IT auditors who want to expand their responsibilities into Security Management, risk governance, and policy design, adding depth to audit reports and recommendations.
3. Certified in Risk and Information Systems Control (CRISC)
Also offered by ISACA, the Certified in Risk and Information Systems Control (CRISC) certification is designed for professionals who design, implement, and maintain IT Risk Management and control frameworks. It's highly regarded for its focus on aligning IT risks with overall business strategy.
Holding a CRISC shows that you can identify and evaluate IT risks and build effective controls to mitigate them. That's a vital skill set for any risk-based IT audit.
4. Certified Information Systems Security Professional (CISSP)
The Certified Information Systems Security Professional (CISSP), offered by ISC2, is a globally recognized certification for experienced security professionals. It covers a broad range of topics including security operations, asset security, and Risk Management.
While CISSP is primarily a security certification, it complements IT audit work by providing strong technical foundations. Many senior auditors and security consultants hold both CISA and CISSP to cover both audit processes and in-depth technical reviews.
5. ISO/IEC 27001 Lead Auditor
The ISO/IEC 27001 Lead Auditor certification qualifies you to plan, perform, and manage audits of Information Security Management Systems (ISMS) based on the ISO/IEC 27001 standard. It is offered by various accredited bodies worldwide.
This certification is a must-have if your organization works with ISO frameworks or is going through an ISO 27001 audit and needs to demonstrate compliance to clients and regulators. It equips you with practical auditing skills and an understanding of global best practices for securing information assets.
Frequently asked questions
How often should an IT audit be performed?
Most organizations run a comprehensive IT audit once a year, with focused reviews on high-risk areas every quarter. Regulated industries may need more frequent audits to meet compliance schedules.
How long does an IT audit take?
A small business audit usually takes 2 to 5 days. Mid-market audits run 1 to 3 weeks. Enterprise audits can take 4 to 8 weeks or longer, depending on scope.
Who should own the IT audit?
Internal audits are typically owned by the IT director or compliance officer, with execution carried out by the IT audit team. External audits are owned by the third-party firm but require a designated internal point of contact.
What are the 7 audit procedures?
The most commonly referenced procedures are inquiry, observation, inspection, recalculation, reperformance, confirmation, and analytical procedures.
What is the difference between an IT audit and an internal audit?
An internal audit is a broad review of an organization's controls and processes. An IT audit is a specific type of audit focused only on technology systems, data, and IT-related controls.

Read other articles like this one: